Auditoria De Segunda Parte

How second-party audits actually work when you're the supplier getting grilled
Most people think auditoria de segunda parte is just an internal audit with a guest reviewer. That's wrong and thinking that way will get you blindsided. A second-party audit happens when someone you do business with sends their own people to check your operations. They are not neutral. They are there to protect their interests while checking whether you meet contractual requirements. This matters more than you might realize because the dynamics are completely different from a third-party certification audit. I had a supplier bring their quality manager to my facility last year for exactly this kind of audit. Everything seemed fine on paper. Their checklist was thorough, which is standard. But here is what nobody tells you about these audits: the auditor you are dealing with often has dual objectives that conflict with each other. They need to verify compliance while also gathering ammunition for future contract negotiations. When they find a nonconformity, it is not just a finding. It is leverage. I learned this the hard way during that 2019 engagement when a minor documentation gap got inflated into a systemic process failure because their regional VP had been shopping around for reasons to renegotiate our pricing. The workaround I used was straightforward. I asked them in writing, before any closing meeting, to identify exactly which contract clause each observation mapped to. This forced the findings back into contractual territory instead of letting them drift into subjective complaints. It changed the entire tone of the audit from day two.
What you need to prepare for auditoria de segunda parte
Start by understanding what distinguishes this from other audit types. A first-party audit is your own internal check. A third-party audit comes from an independent body like a certification agency. A second-party audit sits somewhere in between, and that in-between status creates specific risks. The auditor is technically objective, but financially and relationally aligned with the organization that hired them. They will not sabotage you deliberately, but they will also not go out of their way to help you either. Your job is to make verification as easy as possible so there is no reason for them to dig deeper. The practical preparation takes about two weeks for a standard manufacturing or service operation. First, gather every procedure, work instruction, and record that your customer referenced in the contract. Not everything your company has. Just what they asked for. Then do a pre-audit walkthrough yourself, ideally with someone who has never seen the area before. You will spot things immediately that your team has normalized over months or years. I usually budget four hours for a facility of roughly two thousand square meters with a production line and a warehouse. This is not guesswork. We tracked this across twelve audits and the variance was minimal. One thing that surprises people is the document control piece. Second-party auditors almost always check document revision status first. If your procedures are outdated even by a few months, they will use that as evidence of a weak quality management system. This is legitimate from their standpoint, but it is also why your revision history needs to be bulletproof. Make sure every revision note explains what changed and why. Vague entries like "updated per management review" tell them nothing and raise more questions than they answer.
The audit process itself, from opening to closing
The opening meeting is where most suppliers fumble. The auditor will lay out their agenda, scope, and methodology. This is your chance to clarify boundaries. If they say they are auditing the entire production floor, ask whether that includes subcontracted processes or just in-house work. Vague scope definitions lead to scope creep, and scope creep leads to surprise findings in areas you were never prepared to discuss. I recommend writing down every boundary discussion point and having both parties initial it. It sounds formal but it saves three hours of argument at the end. During the audit itself, the typical flow involves document review, process observation, and interviews. Document review usually takes thirty to forty percent of total time. Process observation takes forty to fifty percent. Interviews take the rest. If your auditor spends more than sixty percent of their time on interviews, something is wrong with your documentation or your processes do not match your documents. Either way, you have a problem. Here is a detail most guides miss. The way auditors sample evidence changes depending on whether they are looking for confirmation or nonconformity. When they are in confirmatory mode, they look for evidence that supports what you claim. When they switch to investigative mode, they look for evidence that contradicts it. You can usually tell which mode they are in by their body language and questioning style. Confirmatory auditors ask "show me how this works." Investigative auditors ask "what happens when this goes wrong." Once I noticed an auditor shift from one style to the other mid-interview, I paused and asked if they had found something concerning. They admitted they had. We resolved it together before it became a formal finding. This is an unusual level of transparency on their part, but it happens more often than you would think when you treat the auditor as a collaborator rather than an adversary.

Common pitfalls and what actually goes wrong
The biggest mistake companies make is treating a second-party audit like a third-party audit. Third-party auditors follow standards like ISO 9001. Second-party auditors follow your customer's requirements, which may include standards, but also include proprietary processes, delivery metrics, and performance targets that have nothing to do with quality management systems. If you only prepare for ISO clauses, you will walk into a wall of findings about traceability, packaging standards, or reporting formats that your customer expects but nobody told you about explicitly. Another pitfall is underestimating how much access the auditor will request. They will ask for personnel interviews, raw access to records, and unsupervised walkthroughs. Granting this access is important. Restricting it raises red flags faster than any actual nonconformity would. I have seen companies get a major finding simply because the production supervisor refused to leave the room during an interview with a floor operator. The auditor interpreted this as intimidation. Whether it was or not, the perception stuck. There is also the issue of follow-up timelines. Second-party audit reports typically require corrective action plans within ten to fifteen working days. This is shorter than the thirty to sixty days you might expect from a certification body. Plan your response workflow accordingly. Have templates ready before the audit happens. A pre-approved corrective action request form with fields for root cause, corrective action, verification method, and responsible person will cut your response time from hours to minutes once you actually need it.
When second-party audits break down
These audits are not universally effective. The main limitation is that the auditor's competence varies enormously depending on who runs your customer's audit program. Some organizations send experienced quality professionals who understand process mapping and risk-based thinking. Others send procurement staff who treat the audit like a compliance checklist exercise. The difference in outcome for you is significant. With a competent auditor, the engagement is constructive and you leave with genuine improvement opportunities. With a checklist-driven auditor, you leave with a list of technicalities that feel arbitrary but must still be addressed. There is also the problem of audit fatigue. If you have multiple customers conducting second-party audits on the same processes using different checklists, you end up with overlapping requirements and conflicting expectations. This is especially common in industries like automotive and medical devices where tiered supply chains are the norm. One workaround is to maintain a master traceability matrix that maps every customer requirement to your internal controls. When a new audit comes in, you can quickly show which existing controls satisfy their questions rather than rebuilding explanations from scratch each time. This matrix itself becomes a living document that your team should review quarterly, not just before an audit window. The other realistic limitation is that second-party audits tend to focus on the past. They verify whether you have been doing what you said you would do. They rarely assess whether your system is capable of adapting to future changes. If your customer cares about continuous improvement and innovation readiness, a second-party audit alone will not give you that assurance. You would need to supplement it with a third-party certification audit or an internal strategic review to cover that dimension adequately.
A practical example from recent experience
Last quarter I dealt with an auditor who insisted that our calibration records for a specific torque wrench were insufficient because the certificate only listed the nominal value and tolerance but not the actual measured value at the point of use. Our calibration provider followed standard ISO 17025 practice, which requires certifying at the points specified in the procedure. We had specified the full range in our procedure. The auditor wanted us to add a dedicated calibration point at the exact torque value we use most frequently. This is a legitimate concern in theory, but in practice it meant recalibrating the wrench at a single point rather than across its range, which would have degraded the accuracy assessment. The solution was not to argue. It was to pull our calibration procedure, the torque wrench specification sheet, and the calibration certificate and lay them side by side. Then I calculated the measurement uncertainty at the point of highest usage and showed that it fell within acceptable bounds relative to the tolerance. The auditor accepted this after about twenty minutes of review. The key was having the calculation ready rather than trying to do it on the spot. I now include this specific analysis in our standard audit packet for any customer who audits torque-controlled processes. If you are preparing for an upcoming second-party audit, the single most effective thing you can do is read your contract and customer requirements document line by line before anything else. Everything else builds on that foundation. Skip it and you will be responding to requirements that nobody explicitly wrote down but everyone implicitly expects.

Galeria
-
Auditoría de Segunda Parte en IATF 16949 | PDF | Auditoría | Calidad ... -
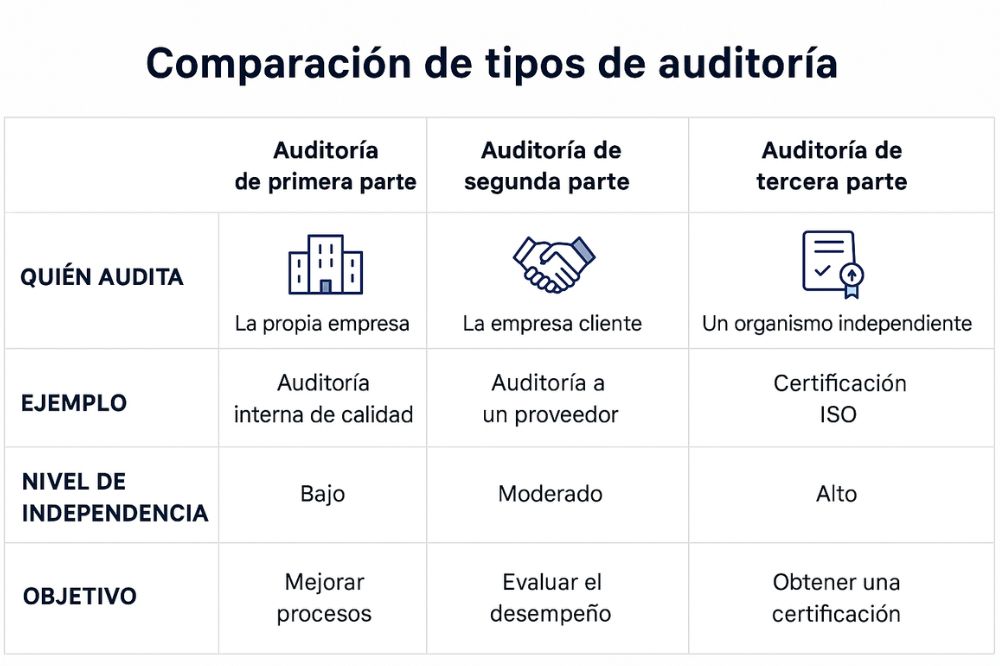
Auditorías de segunda parte: evalúa a tus proveedores - Blog ATM -
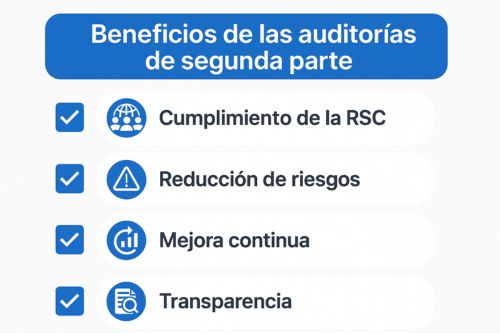
Auditorías de segunda parte: evalúa a tus proveedores - Blog ATM

